New Delhi, October 30, 2026 (Yes Punjab News)
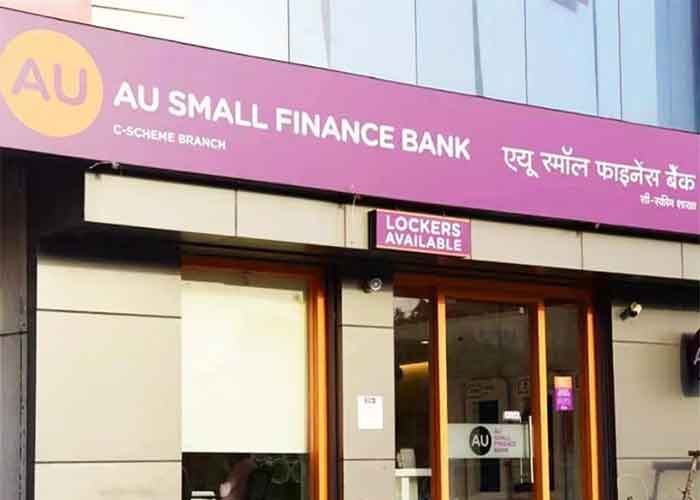
AU Small Finance Bank on Friday said it was investigating a potential data leak involving a software-as-a-service (SaaS) platform managed and hosted by Salesforce after a hacker group claimed to have breached the lender’s systems and accessed sensitive customer information.
In a statement, the bank said it was examining a possible data leak linked to a Salesforce-managed platform containing limited information related to vehicle loan customers.
“AU Small Finance Bank is investigating a potential data leak involving a software-as-a-service (SaaS) platform managed and hosted by Salesforce, which holds limited data relating to our vehicle loan customers,” the bank said.
However, the lender clarified that its own systems had not been affected and that all banking services continued to operate normally.
“We reaffirm that the bank’s own systems remain unaffected and all banking services are operating normally,” the statement added.
The development follows reports that the hacking group ScarlettGroup had claimed responsibility for an alleged breach involving AU Small Finance Bank.
According to the group’s claims, the alleged threat actor obtained customer and internal corporate data, including Know Your Customer (KYC) records, personal identification documents, PAN and Aadhaar details, credit reports, bank statements, loan applications, signed agreements, insurance records, customer relationship management (CRM) data, employee information, login histories and audit logs.
Following the reports, shares of AU Small Finance Bank traded around 2 per cent lower at Rs 860.45 apiece on the BSE on Friday.
According to exchange data, the stock recorded a 52-week high of Rs 1,144.65 and a 52-week low of Rs 832.
Earlier in October, state-owned State Bank of India (SBI) experienced a data breach, with 3,897 customer records reportedly found exposed on the dark web.
The public sector lender had received communications from its Threat Intelligence Service Provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In) regarding an alert about the suspected exposure of customer data.
 FOLLOW NOW