Ahmedabad, August 31, 2026 (Yes Punjab News)
While India was carrying out Operation Sindoor in May 2025 following the Pahalgam terror attack, a parallel cyber campaign was underway against Indian government websites, with investigators later describing the attempted attacks as an effort aimed at disrupting critical digital infrastructure.
More than a year after the Gujarat Anti-Terrorist Squad (ATS) uncovered the case, the National Investigation Agency (NIA) has expanded its probe, conducting searches at five locations across Maharashtra, Gujarat, Telangana, Bihar and Delhi on August 24.
The NIA said the case involves attempted Distributed Denial-of-Service (DDoS) attacks against 54 websites belonging to Central government entities during Operation Sindoor. The targeted systems included critical computer resources and Critical Information Infrastructure (CII), with investigators alleging that the activity was intended to undermine national sovereignty, security and unity and create public fear.
During the searches, officials seized three laptops, five mobile phones, pen drives and other digital devices, besides documents containing allegedly incriminating material related to hacking activities. Several individuals identified through technical analysis as having allegedly assisted the accused were also examined.
The investigation began after the April 22, 2025, terror attack in Pahalgam, Jammu and Kashmir, in which 26 people, including a Nepali citizen, were killed. India subsequently launched Operation Sindoor, with the armed forces striking nine terrorist infrastructure sites in Pakistan and Pakistan-occupied Kashmir during the intervening night of May 6 and 7.
The cyber activity being investigated intensified around the same period.
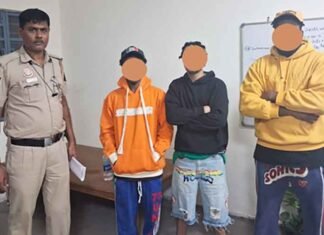
According to the Gujarat ATS, 18-year-old Jasim Shahnawaz Ansari of Nadiad and a juvenile were involved in attempts to target Indian government websites through DDoS attacks. Investigators had been monitoring anti-national activity on social media and the Dark Web when they received information about Ansari and other juveniles allegedly linked to a Telegram group called Anonsec.
The group had earlier operated through channels identified as EXPLOITXSEC and ELITEXPLOIT, using Telegram identities including @BYTEXPLOIT and @YourMindFvcker. Investigators found that its members used programming tools and applications such as Termux and Pydroid3, while obtaining DDoS scripts from GitHub.
The alleged modus operandi involved directing large volumes of traffic towards targeted websites and then checking their accessibility through CheckHost.net. Screenshots and claims of successful attacks were subsequently shared on Telegram.
The ATS said more than 50 government and state government websites were targeted between April and May 2025. On May 7, when Operation Sindoor was launched, the group allegedly planned attacks on 20 Indian government and state government websites.
Telegram posts attributed to the group claimed that Indian websites and servers had been taken down.
However, the subsequent investigation found a gap between those claims and the group’s actual technical capability.
Gujarat ATS SP K. Siddharth told IANS that the accused had attempted to disrupt the websites but lacked sufficient computing and server capacity to sustain an attack capable of overwhelming government infrastructure.
“They were not breaching per se, it was an attempt to take down the websites,” Siddharth said, explaining that a breach would involve gaining access to data, while a DDoS attack seeks to make an online service unavailable to legitimate users.
According to him, the accused ran scripts to generate traffic towards targeted websites and used CheckHost.net to determine whether the sites were accessible. A temporary loss of accessibility was interpreted by them as evidence that an attack had succeeded.
Their mobile phone-based setup, however, did not have the computational capacity required to maintain a prolonged disruption, Siddharth said.
Investigators nevertheless considered the activity significant because of the evidence recovered from the accused’s devices.
“The material recovered from the accused’s phones, including chats, screenshots and communications, established their intention to target Indian websites,” Siddharth said.
The case was initially registered by the Gujarat ATS under Sections 43 and 66(F) of the Information Technology Act before being taken over by the NIA.
On August 14, 2025, the NIA filed a charge sheet against Ansari, alleging that he had conspired with a juvenile to launch multiple DDoS attacks against Central and state government websites between March and May that year. The agency also said anonymising technologies and encrypted platforms had been used.
The investigation subsequently indicated that the online network extended beyond the two individuals from Nadiad. Siddharth said members of the Telegram group included people of several nationalities, including Bangladesh and Palestine. However, he clarified that the Gujarat ATS investigation did not establish any specific conspiracy linking Pakistan to the attacks.
“There was no specific conspiracy which we could figure out that Pakistan was behind this,” Siddharth said.
He also said investigators did not find evidence of conventional radicalisation that would have warranted invoking the Unlawful Activities (Prevention) Act.
“That is why we did not register under UAPA or anything,” he said.
According to Siddharth, the accused were young people who had largely acquired their technical knowledge through material available online. They were not necessarily highly skilled hackers but had learned to operate scripts and tools.
Much of the activity was carried out through mobile phones, making it difficult for their families to detect, he said.
The latest NIA searches suggest that the investigation continues to examine the wider network behind the attempted attacks. Technical analysis has led investigators to individuals suspected of providing assistance, resulting in searches and the recovery of additional digital evidence.
Although the targeted websites were not brought down for any sustained period, investigators are continuing to examine the intent, coordination, tools and network involved in the attempts.
 FOLLOW NOW